TPRM Questionnaire Library
TPRM Questionnaire Library overview
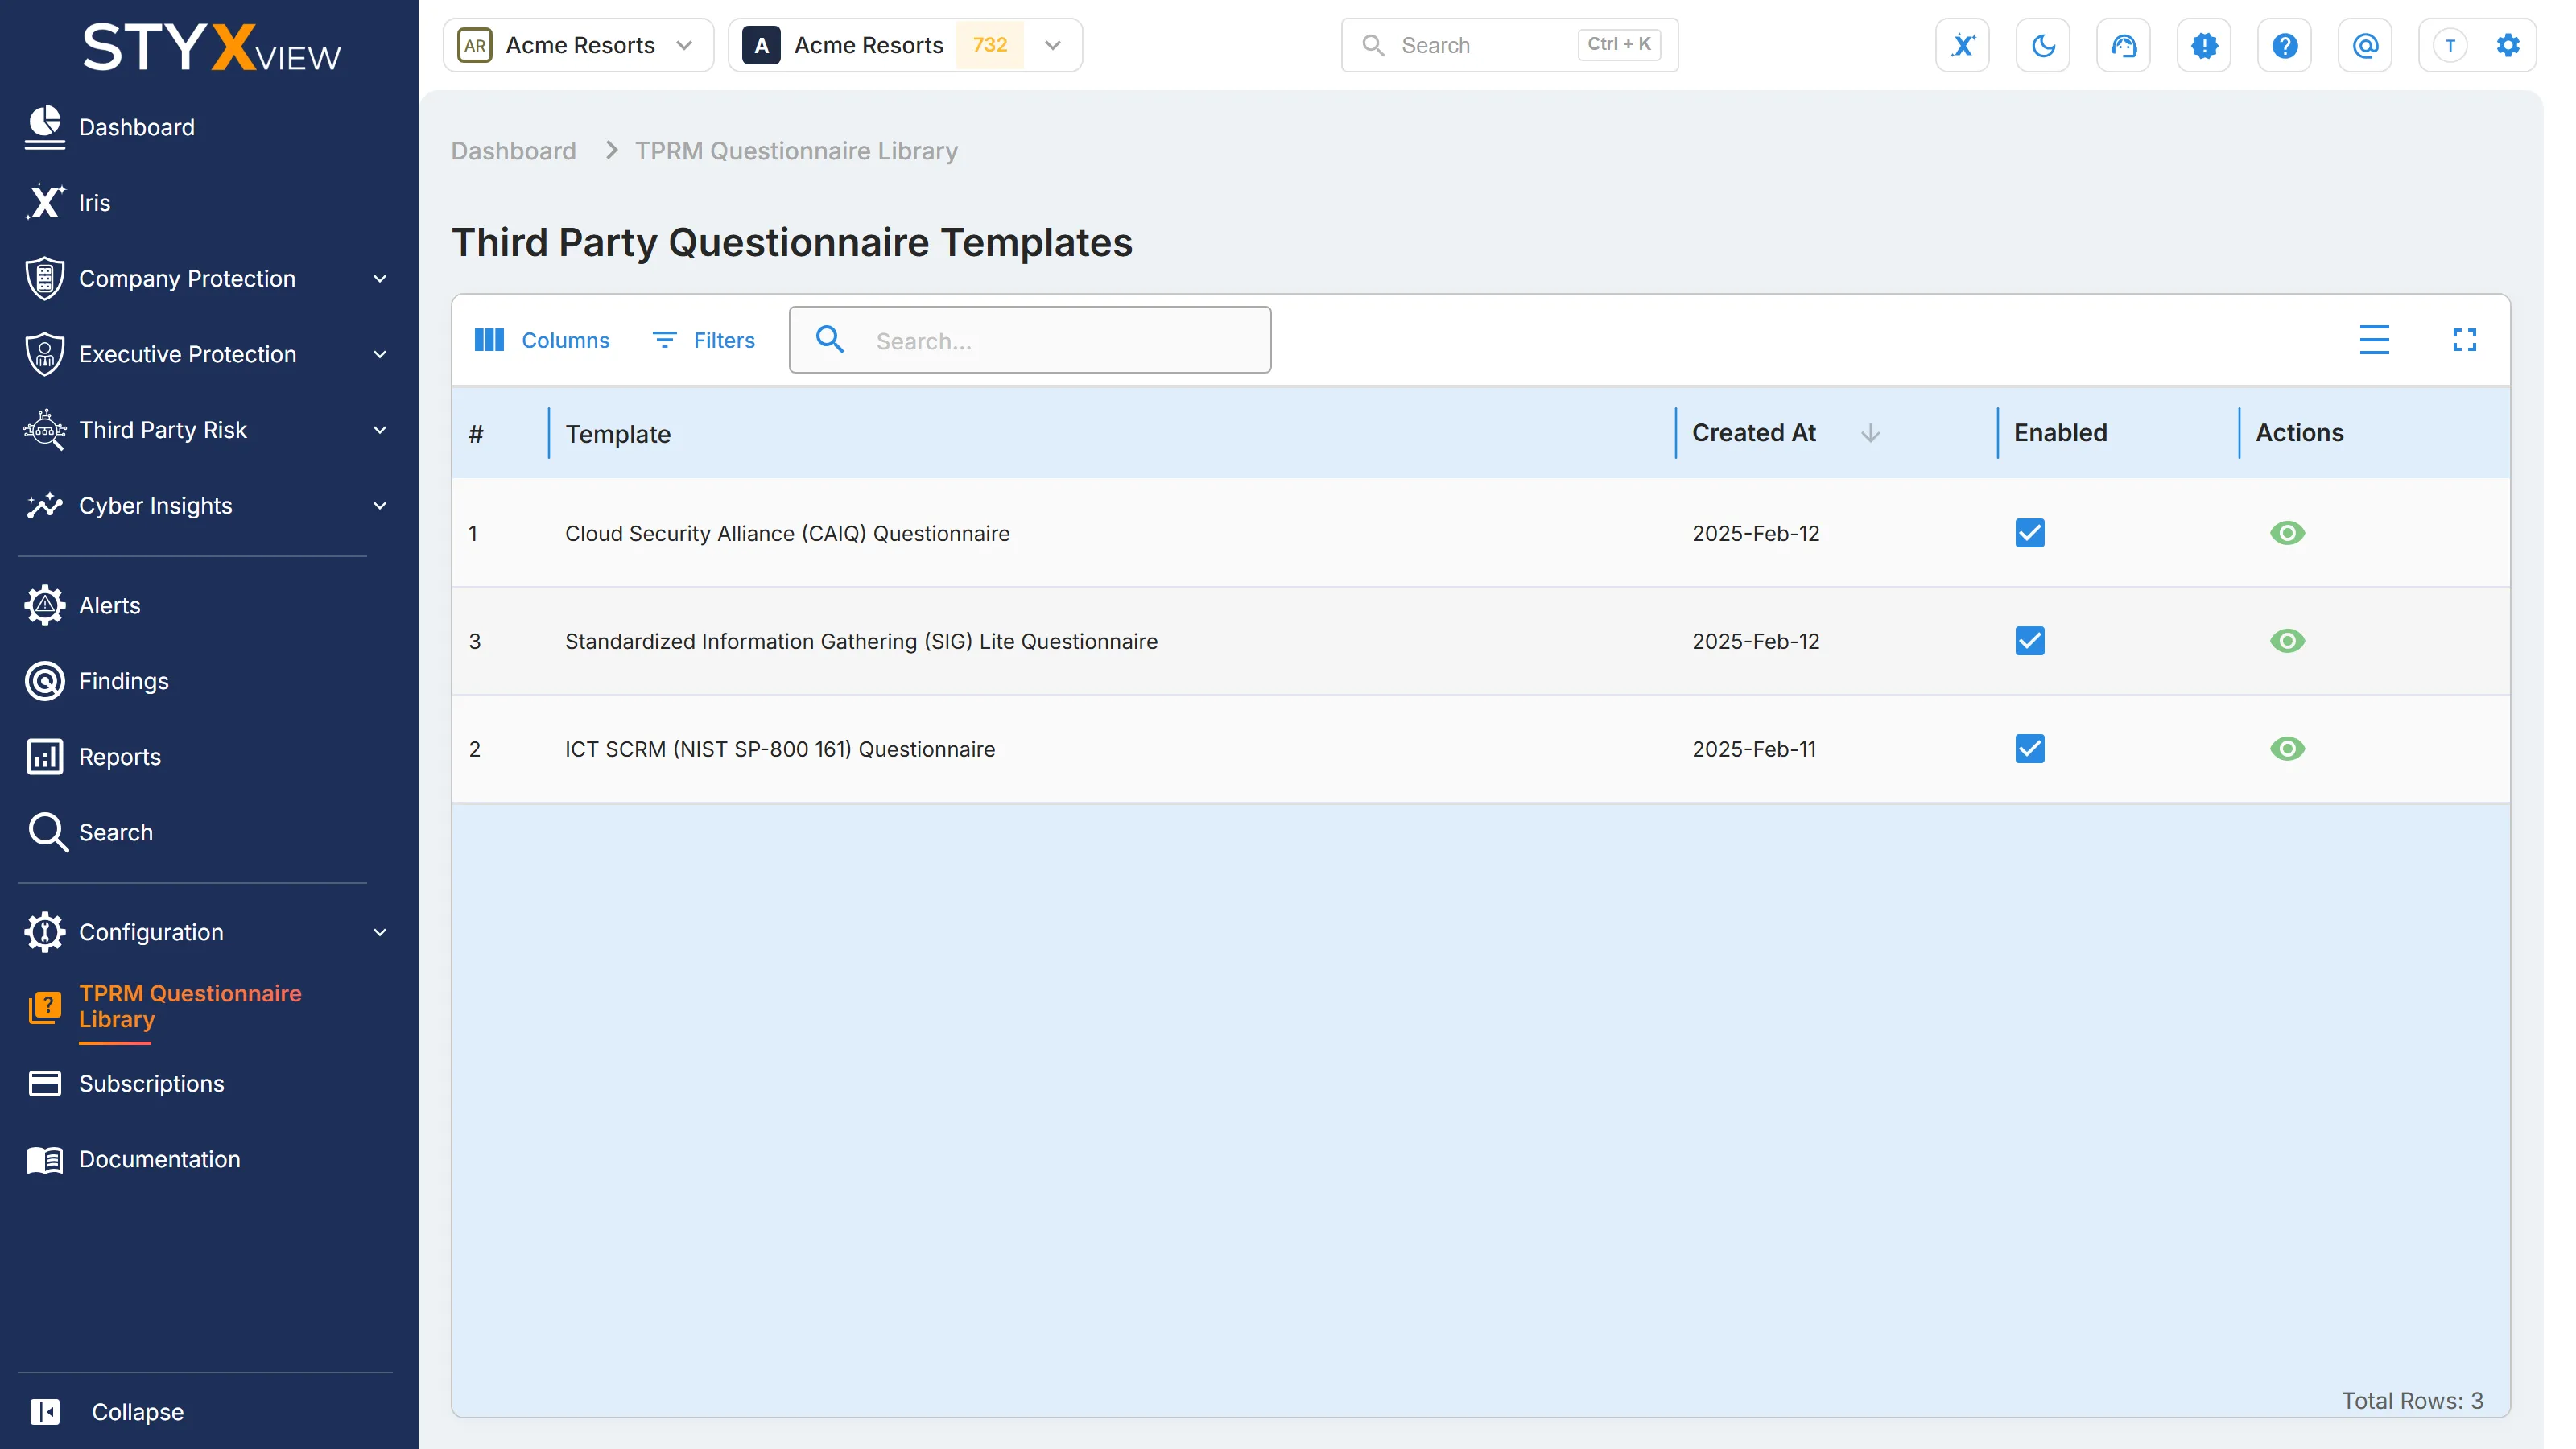
Section titled “TPRM Questionnaire Library overview”The TPRM Questionnaire Library holds the standard questionnaire templates that StyxView provides. Enable a template here to make it available for sending to your third parties.
To open it, select "TPRM Questionnaire Library" in the sidebar. The menu item is shown to Admin users on accounts that include Third Party Risk. You can also reach the library from the "Go to TPRM Questionnaire Library" button on the "Templates" tab of Third Party Risk → Questionnaires.
Understanding the table
Section titled “Understanding the table”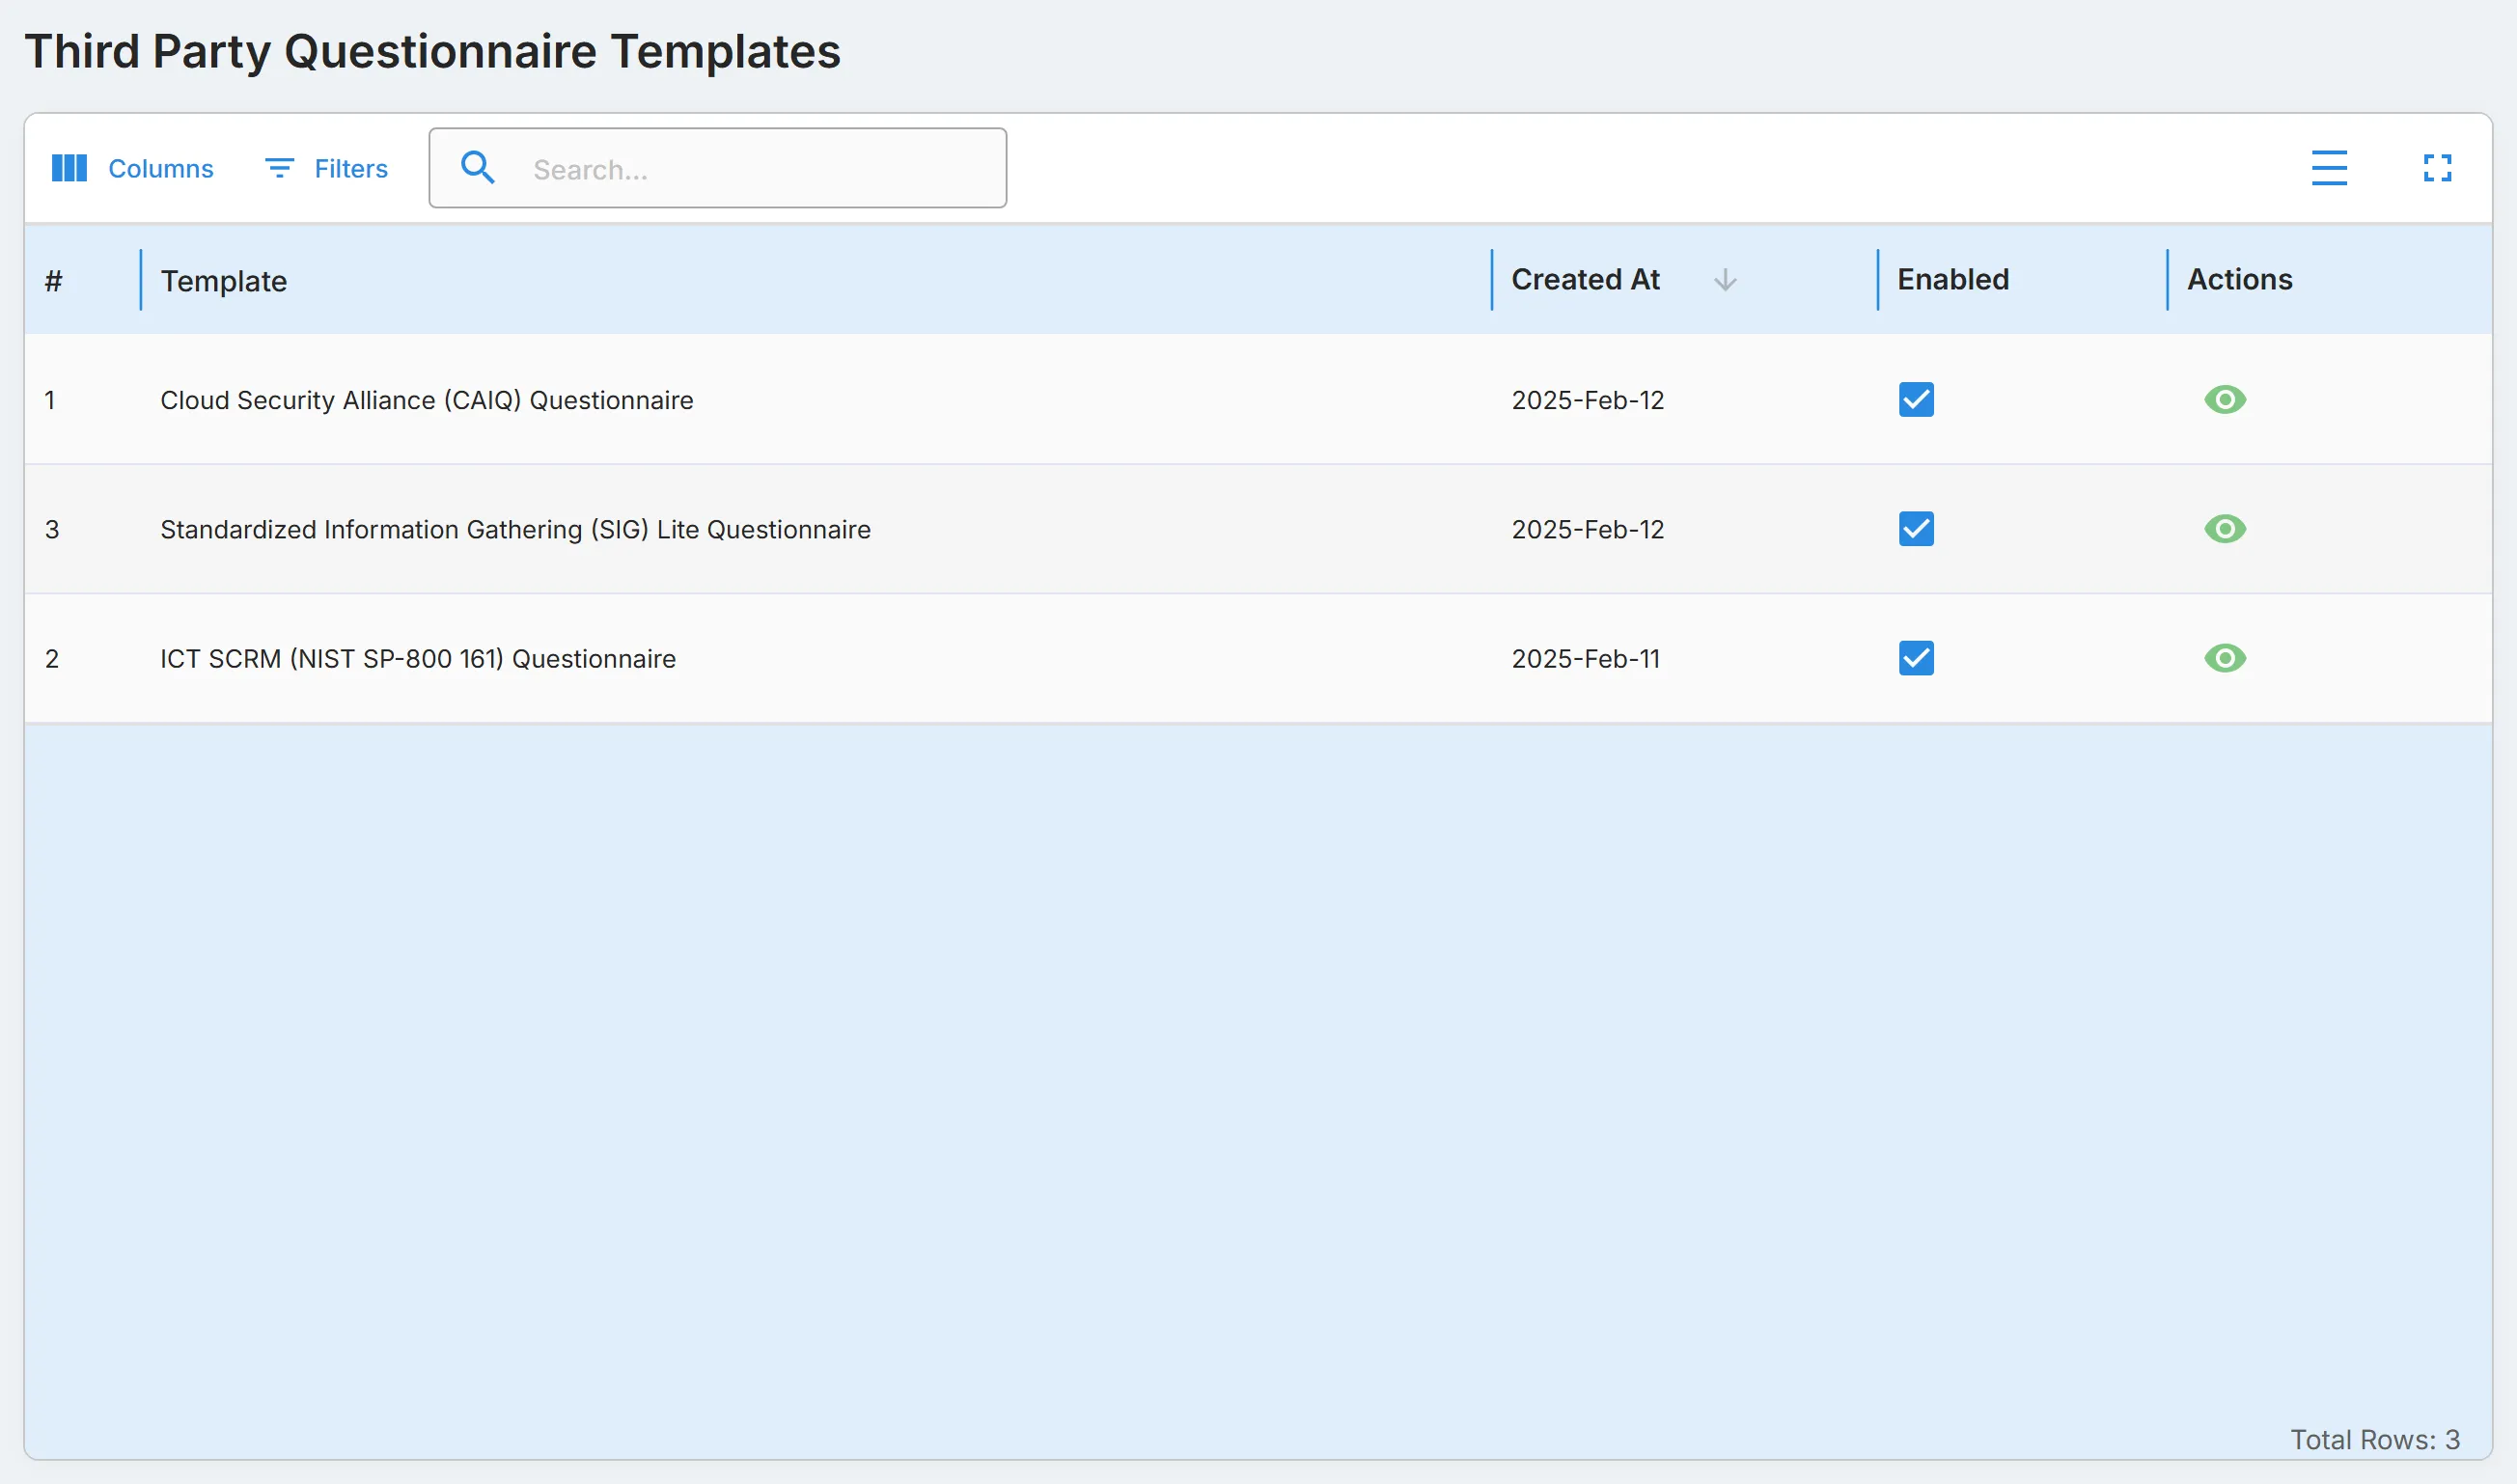
The "Third Party Questionnaire Templates" table has these columns:
| Column | What it shows |
|---|---|
| "#" | The row number. |
| "Template" | The name of the questionnaire template. |
| "Created At" | The date the template was added to the library. |
| "Enabled" | Whether your account can use the template. Select the checkbox to enable it, and clear it to disable it. |
| "Actions" | The view icon opens the whole template. From there, select "Export PDF" to download it. |
When you enable a template, it appears on the "Templates" tab with the type "System", and it is offered in "Questionnaire Template" when you send a questionnaire. System templates cannot be edited. To change one, duplicate it from the "Templates" tab and edit the copy. See Managing Questionnaire Templates.
Templates in the library
Section titled “Templates in the library”The library holds three templates.
-
Cloud Security Alliance (CAIQ) Questionnaire
Description: The Consensus Assessments Initiative Questionnaire (CAIQ) from the Cloud Security Alliance (CSA). It assesses the security controls of cloud service providers and their alignment with cloud security good practice.
Best for: Third parties that provide a cloud service, such as software as a service (SaaS), infrastructure as a service (IaaS), or platform as a service (PaaS).
Documentation link: Cloud Security Alliance (CAIQ) Questionnaire (opens in a new tab)
-
Standardised Information Gathering (SIG) Lite Questionnaire
Description: A shorter version of the full Standardised Information Gathering (SIG) questionnaire. It gives a high-level view of a third party's information security and risk management practices.
Best for: Initial screening, or third parties with little access to sensitive data.
Documentation link: Standardized Information Gathering (SIG) Lite Questionnaire (opens in a new tab)
-
ICT SCRM (NIST SP-800 161) Questionnaire
Description: Based on the National Institute of Standards and Technology (NIST) Special Publication 800-161. It assesses how a third party manages risk in its information and communication technology (ICT) supply chain, also called supply chain risk management (SCRM).
Best for: Third parties that provide critical ICT products or services, especially where your organisation must comply with NIST standards.
Documentation link: ICT SCRM (NIST SP-800 161) Questionnaire (opens in a new tab)
Adding a new template
Section titled “Adding a new template”You can build your own questionnaire at any time with "Create Template" on the "Templates" tab. See Addition of Third Party Questionnaire.
To have a standard template added to the library, email styxguard@styxintel.com (opens in a new tab). It takes 24 to 48 hours for the template to appear on the platform.